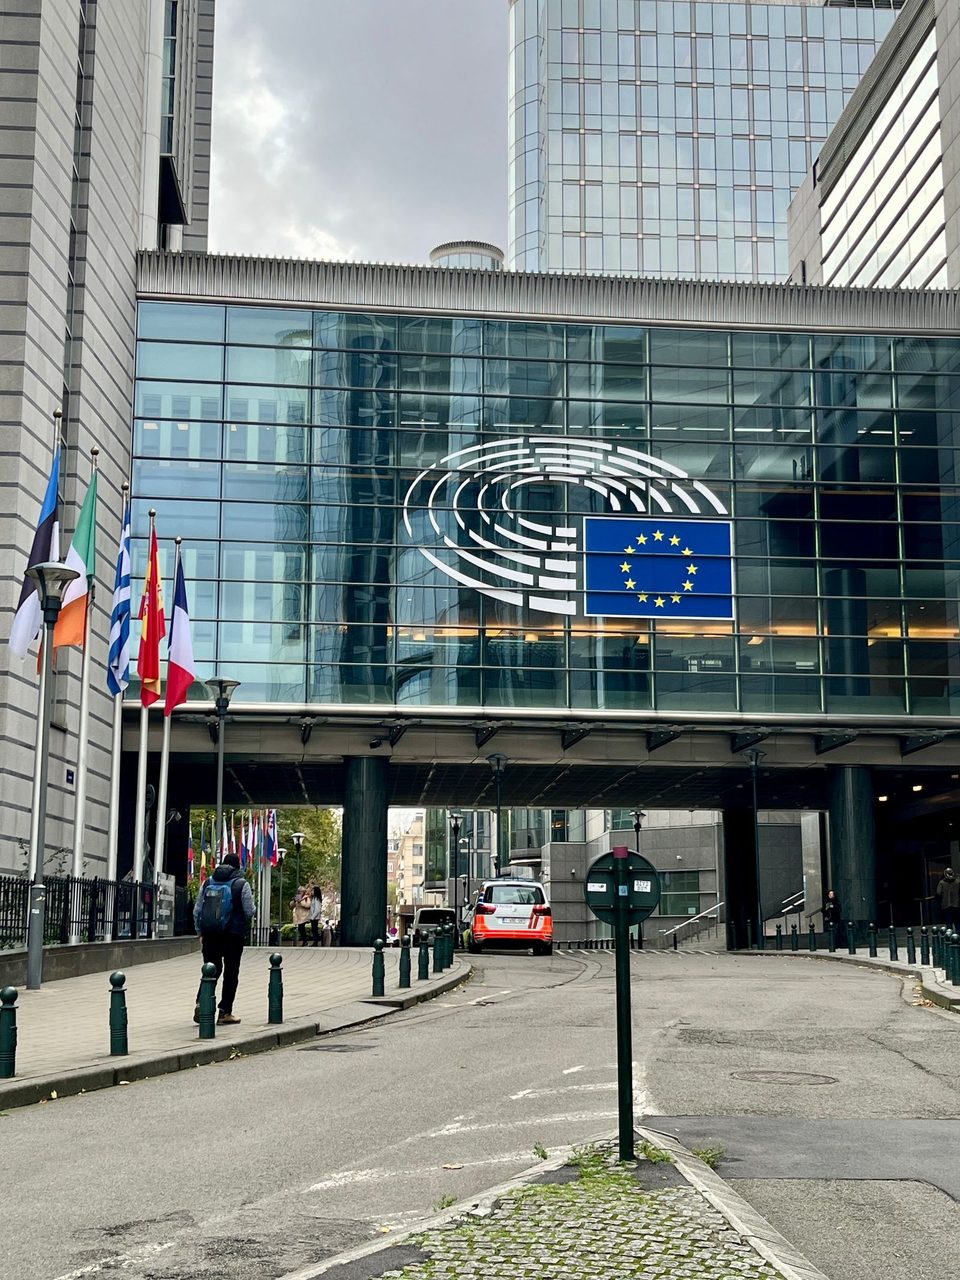
Europe: the comprehensive model
The EU's AI Act is the world's first comprehensive AI regulation, and in 2026 it is moving from text to enforcement. The Act classifies AI systems by risk - unacceptable, high, limited and minimal - and imposes obligations that scale with risk. The first provisions to bite are the bans on unacceptable uses: social scoring by governments, real-time biometric surveillance in public space (with narrow exceptions), and manipulative systems that exploit vulnerability. Companies caught running these systems are now facing real penalties.
The high-risk provisions are the next wave. AI systems used in hiring, credit scoring, education, healthcare and critical infrastructure must meet requirements for data quality, transparency, human oversight and documentation - and must pass a conformity assessment before deployment. For general-purpose models - the frontier foundation models - the Act imposes transparency duties: disclose training data sources, publish safety evaluations, and mark AI-generated content. The result is that any company deploying AI in Europe now has a compliance checklist, and the checklist is not trivial.
The Act's enforcement is designed to be serious. Each member state has a national supervisory authority, and the European AI Office coordinates cross-border cases. Fines scale with company size, reaching up to 7% of global turnover for the worst violations. The first investigations are underway, and the legal test cases are being argued. Europe's bet is that a clear, enforceable rulebook will make it the 'trustworthy AI' market - at the cost, critics say, of slowing innovation and pushing some companies to launch outside Europe first.
America: the voluntary framework
The United States has chosen a fundamentally different path: no comprehensive federal AI law, but a sprawling ecosystem of executive orders, agency rules, state laws and industry self-regulation. The federal approach is risk-based and targeted: agencies regulate AI within their existing authority - the FTC for consumer deception, the FDA for medical AI, the CFPB for financial algorithms - rather than through one overarching statute. The AI Bill of Rights framework, issued as guidance, sets principles for safe, non-discriminatory systems, but it is voluntary.
The state level is where US action is most concrete. Colorado passed the first comprehensive state AI law, and a dozen more states have followed with requirements for algorithmic impact assessments, disclosure of AI in employment decisions, and protections against AI-driven discrimination. The patchwork is inefficient - companies face different rules in different states - but it is also an experiment in what works, and the federal conversation is learning from it.
The enforcement reality is driven by the FTC, which has taken a series of high-profile actions against AI products it considers deceptive - from fake reviews generated by AI to tools that facilitate fraud. The FTC's theory is that existing consumer-protection law applies to AI regardless of the technology, and it has won cases on that theory. The message to companies is clear: you can deploy AI, but you cannot use it to lie to people - and the agency is watching.
China: the safety-first model
China's approach is the most directive of the three. It regulates AI through sectoral rules - separate regimes for deepfakes, algorithmic recommendation, generative AI and biometric identification - administered by multiple agencies. The generative-AI rules require content to align with state values, mandate content moderation, and impose real-name registration for providers. The algorithmic rules require recommendation systems to be transparent, allow users to opt out of personalised feeds, and prevent 'addictive' designs.
China is also the world leader in AI governance infrastructure: its large-scale model registry requires developers to file before release, and its evaluation systems benchmark models for safety and capability. The Chinese framing is 'development with governance' - regulation designed to keep AI safe and aligned with state priorities while aggressively promoting the industry. The tension between promotion and control is real, and the direction has been consistent: the government is the planner, the safety bar is high, and the room for autonomous innovation is bounded.
The international dimension of China's approach matters beyond its borders. Chinese open-weight models are among the most widely used in the world, and they carry the assumptions of the Chinese governance model - content filtering, alignment practices and reporting obligations baked into the training and release process. Developers who adopt these models inherit a governance regime they did not choose. The open-weights movement, in other words, is exporting not just technology but a model of governance.
The emerging international standards
Below the national laws, a layer of international standards is forming. The OECD's AI principles - adopted by 40+ countries - provide a common vocabulary and baseline expectations. The Council of Europe's Framework Convention on AI is the first binding international treaty on AI, covering human rights, democracy and the rule of law. And the technical standard-setting bodies - ISO/IEC - are publishing the standards that conformity assessment will reference: risk-management frameworks, bias-testing methods and transparency requirements.
The standards matter because they make regulation interoperable. A company that certifies against an ISO standard can show compliance across jurisdictions; a regulator that references the same standard can accept the assessment. The emerging architecture is: national law sets the requirements, international standards define how to meet them, and conformity assessment bodies verify. It is the same architecture that regulates cars, planes and medical devices - and it is being built for AI at unprecedented speed.
The G7's 'Hiroshima process' and the international AI safety summits have added a diplomatic layer: agreements on common safety thresholds for frontier models, reporting of serious incidents, and cooperation between AI safety institutes. The safety institutes - the UK's AISI, the US's US-AISI and their European and Asian counterparts - are running shared evaluations and publishing comparative results. The cooperation is real, but it is coordination, not command: each country still sets its own rules.
What the patchwork means for builders
For companies building AI products, the practical consequence of the patchwork is a compliance burden that varies by market. The default strategy for global companies is 'comply with the strictest' - build to the EU standard, apply it everywhere, avoid regional variations where possible. The cost is real: risk assessments, documentation, content-labelling and human-oversight processes add engineering and legal overhead. The alternative - separate products for separate markets - is worse, because it fragments the product and the team.
The strategic implication is that AI capability and AI compliance are converging. The models that pass the hardest safety evaluations, the systems that document their data and decisions, the companies that can prove what their AI does - these are becoming the default, not the exception. The frontier labs already operate this way; the pressure is spreading to every company that deploys AI in a regulated market. In 2026, 'trustworthy AI' is no longer a slogan - it is a compliance requirement with teeth.
What the patchwork means for users
For individuals, the patchwork is a mixed blessing. In Europe, you have enforceable rights: the right to know when you are interacting with AI, the right to human review of high-stakes automated decisions, the right to object to profiling, and real remedies when companies break the rules. In the United States, your protection depends on your state and on the FTC's appetite. In China, the state's protection framework is strong but the rights are framed within a different system of governance.
The practical advice for users is to assume AI is everywhere and verify accordingly: check whether the support agent is a bot, read the terms on how your data trains models, and treat AI-generated content with appropriate skepticism unless it is clearly labelled. The regulation is moving in your direction - transparency requirements are the common thread across every regime - but the enforcement is young, and personal vigilance remains the most reliable safeguard.
The next phase
The next phase of AI regulation will be defined by three developments. The first is enforcement: the EU's first fines, the FTC's next actions and China's ongoing audits will set the practical boundaries of what is allowed. The second is convergence: as international standards mature, the patchwork will consolidate around common technical requirements even as the political framing differs. The third is the frontier question: as models grow more capable, whether the current rules can keep up - or whether the most powerful systems demand a fundamentally different governance regime.
The honest summary for 2026: AI regulation has moved from debate to reality, the world is experimenting with three different models, and no one knows yet which will prove best. What is certain is that the era of unregulated AI is over. The question now is not whether AI will be governed, but how - and the answer is being written in Brussels, Washington, Beijing and the standards bodies of Geneva, one rule at a time.
The enforcement machinery in practice
The difference between a law on the books and a law in force is the enforcement machinery, and 2026 is the year AI enforcement stopped being theoretical. The European Commission has established the AI Office, which coordinates investigations, manages the general-purpose-model rules and maintains a registry of the most capable systems. The member-state authorities are running conformity assessments on high-risk systems, and the first enforcement actions are underway - against a major platform for inadequate content labelling, against a hiring tool for discriminatory outcomes, and against an AI medical device for insufficient documentation.
The enforcement style is evolving through practice. The early cases show the regulators prioritising the systemic failures - the algorithms that harm people at scale - over paperwork errors, and the remedies going beyond fines to include structural changes: redesign the system, submit to audits, publish the evaluations. The agencies are also cooperating across borders, sharing findings and coordinating actions, which means a company cannot simply move its headquarters to escape scrutiny. The practical message to the industry is that the rules are real, the inspectors are trained and the first decisions are starting to set precedent.
The private enforcement layer is also growing. Class-action lawyers have discovered AI as a target, and the first cases are being filed on behalf of people harmed by automated decisions - denied loans, denied jobs, denied services - under consumer-protection and anti-discrimination laws. The litigation risk is now a boardroom consideration, and the insurance industry has begun offering 'AI liability' products. The combination of public enforcement and private litigation is what made product liability effective in the twentieth century, and it is being recreated for AI in the twenty-first.
The debate over frontier-model rules
The hardest regulatory question is what to do about the frontier models - the most capable systems at the top of the stack. The debate splits into three positions. The first is the 'capability trigger' view: rules should apply when a model crosses a measurable capability threshold, and models above the line should face extra requirements - evaluations, incident reporting, and possibly licensing. The second is the 'risk-based, not size-based' view: what matters is how the model is used, not how big it is, and regulation should follow the deployment, not the model. The third is the 'no special rules' view: the frontier is not qualitatively different from other software, and general laws suffice.
The European approach has landed on a hybrid: the AI Act's general-purpose-model provisions apply to all foundation models, with 'systemic risk' obligations for the most capable few, defined by computing power and capability. The trigger has been controversial - the compute threshold ages as hardware improves, and the capability measures are contested. The US debate is still largely voluntary, with the safety institutes running evaluations but without binding triggers. China applies its registration and content rules to all large models regardless of capability.
The open-weights dimension makes the frontier question harder still. A frontier model released with open weights cannot be recalled, re-licensed or restricted after the fact - the capability is permanently in the wild. The policymakers' options narrow to regulating the training inputs (chips, data) and the deployment contexts, rather than the models themselves. This is why the export-control regime and the open-weights debate are two sides of the same question: how to govern a technology whose most important artifacts are weight matrices that anyone can copy.
What builders and users should do now
For builders, the practical checklist is now well established. Map your AI systems and their risk levels; document data sources and processing; implement the transparency requirements (labels for AI-generated content, disclosures for chatbots); run the safety evaluations the standards require; and keep the human-oversight processes that high-risk rules demand. The companies that institutionalise this - not as a compliance exercise but as an engineering practice - will find the cost manageable and the market advantage real.
For users, the advice is to exercise the rights that exist. In Europe, ask for explanations of automated decisions, request human review of high-stakes determinations and complain to the authorities when companies fall short. In the US, check your state's protections and file complaints with the FTC and the state AGs. Everywhere, treat AI outputs with appropriate skepticism, verify consequential claims and keep your own records of what AI told you and when.
The long view is that AI regulation is going through the same maturation every transformative technology experienced - from cars to medicine to finance. The first rules are crude, the enforcement is uneven and the industry complains, then adapts, then builds to the standard. The companies and countries that treat the emerging rules as a design constraint rather than a nuisance will be the ones that build the trust on which mass adoption depends. The regulatory race is just beginning, and it is being run in parallel with the capability race - and the two will shape each other for decades.
The sectoral rules underneath the general frameworks
Below the general AI frameworks sits a dense layer of sectoral rules that, in practice, shape how AI is deployed far more than the headline laws. In finance, the regulators have clarified that AI-driven credit decisions fall under existing fair-lending and fair-credit rules, and the first enforcement actions have targeted discriminatory algorithms. In healthcare, the medical-device regulators require AI tools to be validated like any medical device, with clinical evidence and post-market surveillance - a standard that has slowed the most hyped applications and protected the public from the worst. In employment, the workplace regulators have extended anti-discrimination law to algorithmic hiring, requiring impact assessments and adverse-impact analysis.
The sectoral pattern is consistent: the general frameworks set the principles, and the sectoral regulators turn them into enforceable requirements in the domains they know. The advantage is that domain experts write the rules; the cost is fragmentation and inconsistency - a company that deploys AI across finance, HR and healthcare must navigate three different rulebooks. The trend is toward convergence on common tools - the impact assessments, the bias testing, the documentation - so that a company that builds the capability once can apply it across sectors. The compliance stack is becoming standardised even where the laws are not.
The emerging frontier of sectoral rules is the 'algorithmic systems' legislation: laws that require every AI system that makes significant decisions about people - credit, housing, employment, education - to be logged, tested and explainable. Several jurisdictions are drafting such laws, and the concept is spreading through the international standards. The direction is clear: the era of the 'black box' decision-maker is ending, and the era of the documented, tested, explainable algorithm is beginning. The companies that build transparency in from the start will find compliance cheap; the ones that retrofit will find it expensive.
The economic effects of regulation
The economic effects of AI regulation are contested, and the evidence is still thin, but the early patterns are visible. The compliance cost is real: the largest companies report significant spending on AI governance, and the smallest face a proportionally heavier burden - which is why the small-business exemptions matter. The 'Brussels effect' is real: the EU's standards are becoming the de facto global baseline because global companies prefer one standard to many, and the EU's rules are the strictest. The compliance cost, spread across the global market, is lower than the cost of navigating divergent regimes.
The innovation effects are the crux of the debate. Critics argue that strict regulation slows deployment, raises costs and pushes companies to launch outside the regulated markets - and there is anecdotal evidence of exactly that, with some models and products arriving later in Europe than in the US. Supporters argue that regulation builds the trust that mass adoption requires, and that the 'trustworthy AI' label is a competitive advantage - and the polling shows that consumers are indeed more comfortable with AI where they believe it is regulated. The honest answer is that the net effect depends on the design: badly designed regulation chokes innovation; well-designed regulation channels it.
The market's own response is the most informative signal. The compliance industry is booming - the auditors, the software vendors, the law firms, the consultants - and the AI-governance market is growing faster than the AI market itself. The insurance industry is developing AI liability products. The standards bodies are swamped with work. All of this is the market pricing in the permanence of regulation. Whatever the political swings, the regulatory infrastructure being built now will shape the industry for decades - which is precisely why the design choices of this period matter so much.
The concluding assessment
The honest assessment of AI regulation in 2026 is that the world is building the governance of a general-purpose technology in real time, with all the messiness that implies. The three models - Europe's comprehensive rights-based rulebook, America's sectoral pragmatism, China's state-directed safety regime - are experiments, and none has yet proven superior. The international standards are converging on the technical requirements even as the politics diverge. The enforcement is real and growing. The compliance machinery is being built. And the questions that will define the outcome - the training-data cases, the frontier triggers, the open-weights conundrum - are still being litigated, drafted and argued.
What is certain is that the era of unregulated AI is over, and the shape of the new era is being drawn now. The companies that treat the rules as a design constraint will build products that comply, that users trust and that regulators accept - and they will have a durable advantage. The countries that get the balance right - strict enough to protect, flexible enough to innovate - will host the industry of the future. The regulatory race is running alongside the capability race, and the two are now inseparable. The next decade will be defined by whether the world can govern the most powerful technology it has ever built - and the evidence of 2026 is that it is trying.
Sources & further reading
- EU AI Act - official text and guidance — https://digital-strategy.ec.europa.eu/en/policies/regulatory-framework
- OECD.AI Policy Observatory — https://oecd.ai/
- European AI Office — https://digital-strategy.ec.europa.eu/en/policies/ai-office
- US FTC - AI enforcement actions — https://www.ftc.gov/
- CAC China - generative AI measures (via English coverage) — https://www.cac.gov.cn/
- Council of Europe - Framework Convention on AI — https://www.coe.int/en/web/artificial-intelligence
Frequently asked questions
Which country has the strictest AI regulation?
Europe's AI Act is the most comprehensive and is now being enforced, with risk-based obligations and fines up to 7% of global turnover. China has strict sectoral rules including content moderation and model registration. The US relies on existing law, voluntary frameworks and state-level statutes.
Do AI regulations apply to open-source models?
It depends on the jurisdiction. The EU AI Act has exemptions for research and some open-source models but imposes obligations on those placed on the market. Chinese rules require registration of large models regardless of openness. The open-weights ecosystem is a live regulatory battleground.
What should a small business do to comply?
Start with the basics: know which AI systems you deploy and for what purpose, document your training and data sources where relevant, label AI-generated content, and check whether your use cases fall under high-risk rules in the markets you serve. The safest strategy is to build to the strictest standard you operate under.
Vendor and regulator figures are as published by the organisations above; the analysis and any derived comparison are ours.
Luminesca · Independent analysis · About · Privacy
This page is an informational compilation. For reference only.
Images: Pexels (free license) · Photos by contributors on Pexels.
Privacy Policy